Data Breaches
Prevent Stolen Session Tokens: Technical Controls and Detection
Session tokens often bypass password checks entirely, allowing attackers to maintain access even after you force a global credential reset across all user accounts.
Session tokens often bypass password checks entirely, allowing attackers to maintain access even after you force a global credential reset across all user accounts.
Hashing destroys data irreversibly while encryption hides it temporarily, creating distinct risk profiles for credential storage versus data transit.
Your network allows lateral movement because default protocols trust cached hashes, not because attackers possess superior technical skill or novel exploit methods.
Moving data across borders creates legal exposure even if you use standard cloud services without explicit written consent.
Attackers used three flaws in Ivanti Connect Secure to gain root access, steal credentials and search for Active Directory data on affected networks.
The CPRA adds specific rights to delete and opt-out of data sharing, transforming the CCPA from a notice law into an active control framework with stricter audit rules.
German authorities apply GDPR with rigorous precision, prioritising individual consent mechanisms and detailed accountability records over generic privacy policies.
A valid consumer request forces organisations to audit data flows across third-party vendors, often revealing inventory gaps that standard compliance audits miss.
Most small businesses fail recovery not due to lost data, but because they lack documented procedures for manual business processes during downtime.
Most employee data breaches stem from misconfigured access controls rather than malicious intent, leaving sensitive records exposed to unintended internal viewers.
A total ban on virtual private networks often leaves users with no secure tunnel, exposing their browsing habits to local network operators and state-level surveillance infrastructure.
Mobile devices bypass network perimeter defences, allowing malware to harvest credentials and exfiltrate data directly from the device without triggering standard alerts.
Static scanning fails against fileless attacks, requiring sandboxing to execute code in isolation before delivery reaches the inbox.
Adware creates persistent network noise that masks genuine threats, forcing security teams to waste resources filtering benign but annoying traffic from actual attacks.
Pretexting bypasses technical defences by exploiting human trust, making procedural verification more effective than software filters alone.
Strategic intelligence shifts security from reactive patching to proactive risk management by revealing which adversaries actually target your specific industry and data assets.
Misconfigured baselines create false positives that train defenders to ignore alerts, allowing genuine lateral movement to pass unnoticed during critical incident windows.
Rainbow tables defeat speed-limited brute force by trading storage space for computation time, turning hours of work into instant lookups.
Understanding the human intent behind digital intrusions reveals that technical signatures alone fail to stop determined adversaries who adapt their methods.
Token theft allows attackers to bypass password checks entirely by hijacking the session credential that proves your identity to the system.
The cyber kill chain Lockheed Martin model maps attacker progression, revealing that blocking late-stage actions is often cheaper and more effective than preventing initial entry.
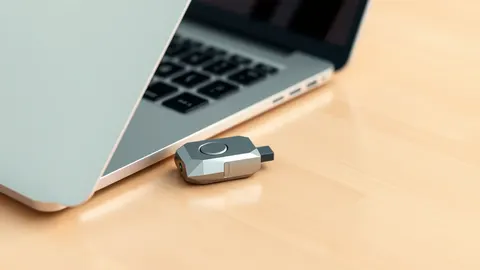
Hardware keys prevent credential theft by requiring physical presence, blocking attacks that bypass passwords and software tokens entirely.
Default credentials bypass encryption and remain active until explicitly changed, creating persistent entry points for automated attacks that ignore standard access logs.
Coordinated vulnerability disclosure shifts the timeline of public exposure, forcing organisations to manage the gap between private research and public patching with precision.